Cyber Pulse: Week 40, 2026
Four vendors confirmed that new flaws were being exploited: Fortinet FortiMail, Cisco Catalyst SD-WAN Manager, Citrix NetScaler (SAML) and Apple CoreGraphics.
Cyber Pulse: Week 40, 2026 Read More »

Four vendors confirmed that new flaws were being exploited: Fortinet FortiMail, Cisco Catalyst SD-WAN Manager, Citrix NetScaler (SAML) and Apple CoreGraphics.
Cyber Pulse: Week 40, 2026 Read More »
Citrix confirmed exploited NetScaler zero-days CVE-2026-88771 and CVE-2026-88772, Bitget reported an about $387.5 million hot and warm wallet incident, and Check Point confirmed active exploitation of CVE-2026-85102 and CVE-2026-93616.
Cyber Pulse: Week 39, 2026 Read More »
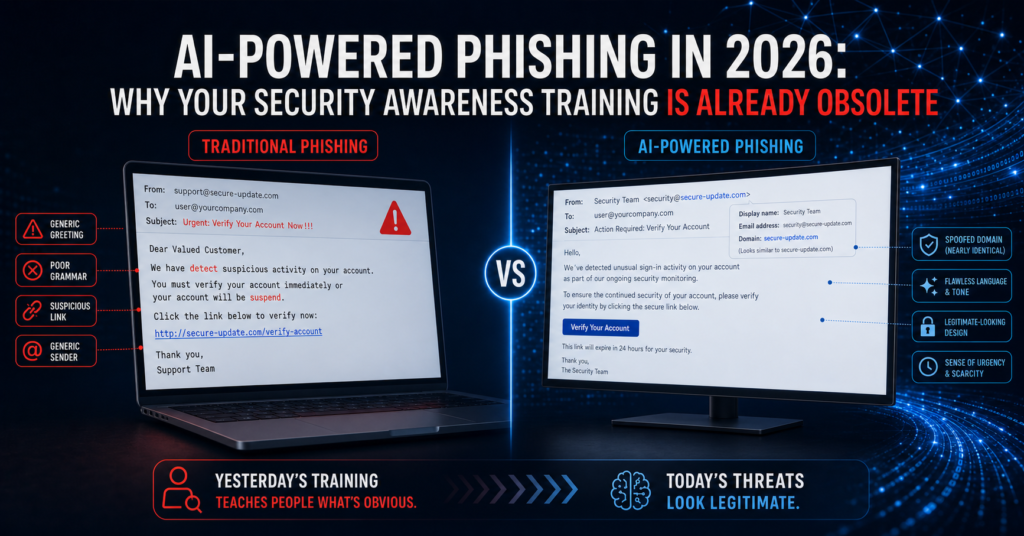
AI-written lures now beat phishing simulations. Why click-rate metrics mislead boards, and the 5-layer defence model CISOs should adopt in 2026.
AI-Powered Phishing in 2026: Why Your Security Awareness Training Is Already Obsolete Read More »
Run AI on your own hardware: Llama 4, Qwen3, DeepSeek, Gemma 3 and Phi-4 compared, plus Ollama and LM Studio and the GPU you actually need.
Running LLMs Locally in 2026 — The Best Options, Tools & Comparison Chart Read More »

Cyber threats are evolving faster than any single analyst can track. Ransomware gangs retool overnight, nation-state actors shift infrastructure in hours, and phishing campaigns now leverage AI-generated content that slips past legacy filters. In this landscape, reactive security is a losing strategy. The answer? Threat intelligence (TI) — the discipline of turning raw threat data

In a world of constant cyber threats, ISO/IEC 27001 has become the global reference point for building and proving an effective information security management system (ISMS). Whether you are a startup handling customer data or a mature enterprise with complex infrastructure, ISO 27001 gives you a structured way to protect information, reduce risk, and win
ISO/IEC 27001 – Introduction and Practical Guidance Read More »
Let me be honest with you. I’ve been through ISO 27001 implementations in the UAE, and I can tell you that the experience here is nothing like what you’ll read in a generic compliance guide. The frameworks are the same, the clauses are the same, the audit process is the same — but the ground
ISO 27001 Implementation Lessons from the UAE — What They Don’t Tell You in the Textbook Read More »
Let me be honest with you. A year ago, most CISOs I spoke with treated AI governance like a “nice to have.” Something for the compliance team to worry about later. Fast-forward to today, and the conversation has completely flipped. Regulations are landing. Boards are asking tough questions. And if you’re in cybersecurity leadership —
AI Strategy and Governance Read More »

In today’s fast-evolving digital landscape, cybersecurity is no longer just a technical necessity — it’s a strategic business enabler. For CISOs and vCISOs, mastering the art of aligning cybersecurity initiatives with core business objectives is key to driving real impact and securing a seat at the executive table. Understanding Business Priorities: The Foundation of Security
How CISOs Can Align Cybersecurity with Business Goals Read More »

Introduction In today’s hyper‑connected world, businesses are navigating a landscape defined by rapid technological change, economic uncertainty, and an evolving threat environment. While innovation accelerates, so do the risks. Cybersecurity, AI adoption, regulatory pressure, and talent shortages are reshaping how organizations operate — and exposing critical weaknesses in their strategy, culture, and infrastructure. This article
The Real Business Pains Companies Face Today — And How Leaders Can Respond Read More »