Blog
Articles
Practical analysis on cyber risk, GRC and AI, written from real programmes in the UAE and GCC. Looking for the weekly brief? See Cyber Pulse.
-
From ISO 27001 to ISO 42001
This is practical guidance. It is not the text of ISO/IEC 27001:2022 or ISO/IEC 42001:2023, and it is not a certificate. Zaheer…
-
The mail gateway is already being exploited. The patch is still upcoming.
Zaheer Ikbal, Founder, CyHelm I would not sit on this one waiting for a patch note. Fortinet published FG-IR-26-175 on 1 October.…
-
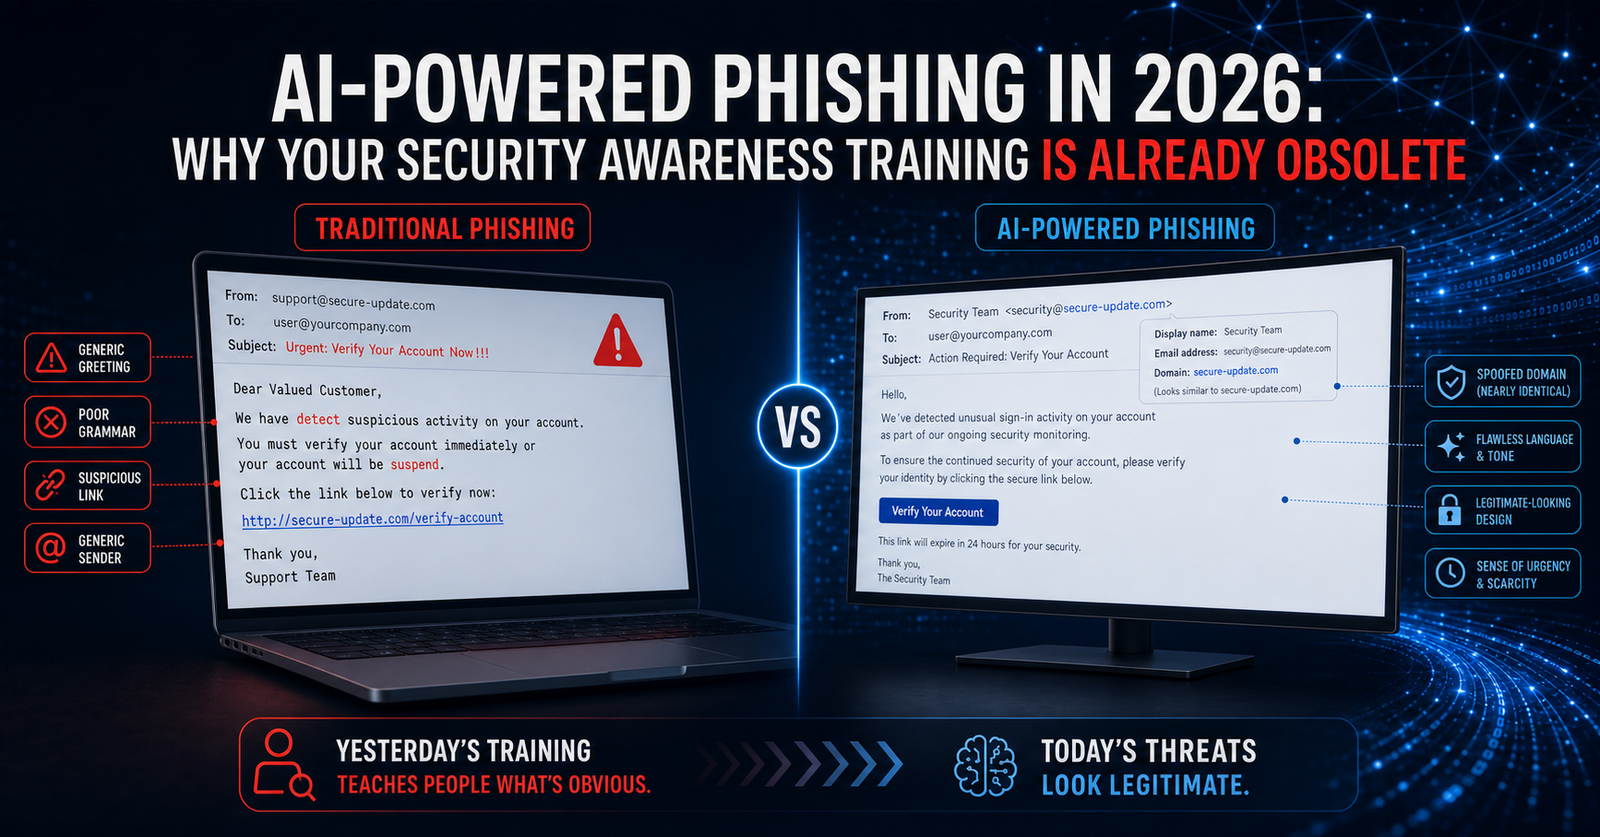
AI-Powered Phishing in 2026: Why Your Security Awareness Training Is Already Obsolete
AI-written lures now beat phishing simulations. Why click-rate metrics mislead boards, and the 5-layer defence model CISOs should adopt in 2026.
-
Running LLMs Locally in 2026 — The Best Options, Tools & Comparison Chart
Run AI on your own hardware: Llama 4, Qwen3, DeepSeek, Gemma 3 and Phi-4 compared, plus Ollama and LM Studio and the…
-
The Ultimate Guide to Threat Intelligence Platforms in 2026: Tools Every Security Team Needs
Cyber threats are evolving faster than any single analyst can track. Ransomware gangs retool overnight, nation-state actors shift infrastructure in hours, and…
-
ISO/IEC 27001 – Introduction and Practical Guidance
In a world of constant cyber threats, ISO/IEC 27001 has become the global reference point for building and proving an effective information…
-
ISO 27001 Implementation Lessons from the UAE — What They Don’t Tell You in the Textbook
Let me be honest with you. I’ve been through ISO 27001 implementations in the UAE, and I can tell you that the…
-
AI Strategy and Governance
Let me be honest with you. A year ago, most CISOs I spoke with treated AI governance like a “nice to have.”…
-

How CISOs Can Align Cybersecurity with Business Goals
In today’s fast-evolving digital landscape, cybersecurity is no longer just a technical necessity — it’s a strategic business enabler. For CISOs and…